

-
November 1, 2026
-
November 1, 2026
The most effective approach to AI agent security on developer workstations is to establish continuous control over the entire agentic environment rather than focusing exclusively on individual AI applications.
For technology companies, this means discovering which agents employees use, understanding the components connected to them, evaluating their permissions, enforcing organizational policies, and monitoring their actions during execution.
Tools such as Claude Code, Cursor, GitHub Copilot, and OpenAI Codex can interact with development environments, access local resources, and participate in workflows involving business systems and proprietary code.
The security implications extend beyond whether an individual application has been approved.
An approved AI coding agent may connect to an unreviewed MCP server, execute instructions from a locally installed Skill, use a personal account, or operate with access permissions that the security organization has never assessed.
From a CEO's perspective, the challenge is balancing the strategic benefits of AI-assisted development with the organization's responsibility to protect intellectual property, maintain operational resilience, and demonstrate effective governance.
The right objective is not to restrict innovation. It is to create the conditions in which AI adoption can expand safely.
Developer workstations occupy a particularly sensitive position within technology organizations.
They are where employees create proprietary software, interact with source-code repositories, configure development tools, and use credentials required for legitimate engineering activities. Sometimes they might even have access to production environments in the cloud, although this goes against most security guidelines.
When AI agents operate in these environments, they may inherit access to resources already available to the developer.
An agent can therefore become an additional participant in workflows that were previously performed directly by a human employee.
This introduces an important distinction: the security risk is determined not only by the application running on the workstation, but also by the instructions it receives, the tools it invokes, and the access available to it.
Consider a developer using an approved AI coding assistant.
The assistant connects to an MCP server that extends its capabilities. The developer installs a community Skill that introduces additional instructions and scripts. A local configuration grants the agent access to files or commands required for its work.
Each element may appear reasonable independently. Together, they can create a security posture that differs materially from what the organization originally approved.
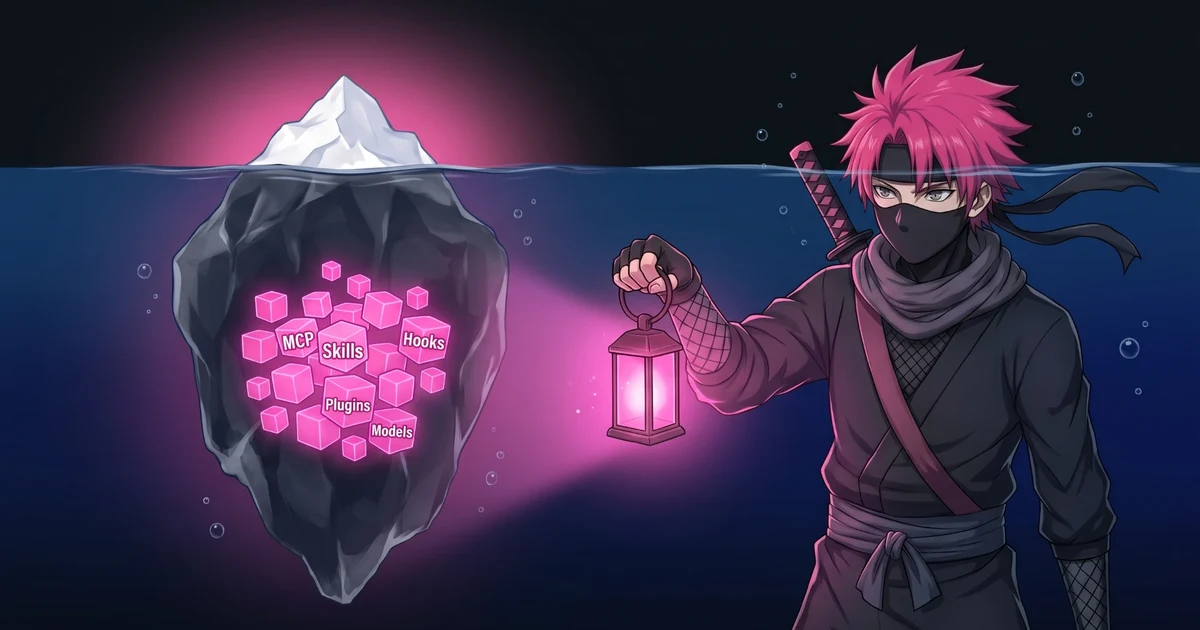
Backslash describes this combination of agents, integrations, tools, and configurations as the agentic AI fabric.
Securing the workstation therefore requires understanding how these components interact, rather than evaluating them as isolated applications.
Organizations cannot govern AI tools they cannot identify.
Backslash's October 2026 enterprise findings report revealed that 79% of assessed organizations described having little to no visibility into their agentic AI inventory.
The problem extends beyond employees installing unauthorized software.
Different employees may configure the same approved agent with different MCP connections, Skills, models, and permissions.
As a result, software procurement records do not accurately represent the organization's effective AI attack surface.
For executive leadership, this creates an accountability gap between officially approved technology and the activities actually occurring across employee endpoints.
Shadow AI includes employees using AI tools that have not undergone organizational review.
However, Backslash identifies another important category: approved agents whose behavior has been changed through unapproved components or local configuration overrides.
This distinction matters because banning unfamiliar applications will not necessarily address risky configurations inside approved tools.
In one enterprise assessment, approximately 35% of roughly 600 detected coding agents were flagged for policy violations.
The implication is clear: governance must extend to the configuration and components of each deployed agent.
AI agents can interact with files and development resources containing sensitive information.
Backslash identified at least one exposed secret, hardcoded credential, or instruction directing credential harvesting in 60% of assessed customer environments.
Examples included credentials embedded in configuration files, agents accessing sensitive environment variables, and prompt-injection instructions attempting to collect secrets.
These risks are especially relevant to organizations whose workstations provide access to valuable intellectual property, customer data, infrastructure, or privileged development systems.
The appropriate response is to inspect both agent permissions and the components that influence agent behavior.
MCP servers provide interfaces through which AI agents can use connected tools and services.
Skills, meanwhile, can introduce reusable instructions and executable scripts into agent workflows.
Both can improve productivity, but their security depends on their implementation, configuration, permissions, and trustworthiness.
An unsafe MCP connection may grant access beyond the intended task. A malicious or poorly configured Skill may instruct an agent to execute commands or transmit sensitive data.
Backslash's enterprise assessments identified an average of approximately 126 MCP servers per organization, with 4.4% of identified servers flagged for security findings.
This demonstrates why MCP and Skill governance cannot remain an optional extension of enterprise AI policy.
When an incident involves an AI agent, traditional records may establish that a process ran or that a connection occurred.
They may not establish which agent instruction, Skill, MCP tool call, or configuration produced the action.
Backslash documented a case in which a security team investigating an agent that had deleted data could not determine which agent was responsible or locate the relevant logs.
For technology companies, the inability to reconstruct agent activity complicates incident response and limits the evidence available for internal governance and audit reviews.
Backslash's platform approach provides a practical framework built around discovery, assessment, governance, protection, and investigation.
The first requirement is a reliable inventory of AI agents and their connected components.
Security teams need to identify the agents installed across endpoints, the models they use, and their associated MCP servers, Skills, hooks, plugins, connectors, and local rules.
Inventory should also account for account identity and whether employees are accessing AI tools through company-managed or personal accounts.
Backslash supports continuous discovery and maps the relationships among these elements.
This allows organizations to move beyond basic application inventories toward understanding what each agent can potentially access and execute.
For executives, the fundamental question becomes: Can our organization accurately identify the AI systems operating on employee workstations?
Once the environment is visible, the next step is evaluating risk at the component and configuration level.
Security assessment should identify excessive permissions, unsafe configurations, exposed credentials, vulnerable or malicious components, and connections that increase the potential impact of agent activity.
Backslash continuously assesses the agentic fabric and maps risks to relevant AI-focused security models.
The important consideration is context.
A component's risk depends partly on what it can reach and how it interacts with other components.
An apparently limited integration may become more consequential when connected to an agent operating with sensitive permissions.
The assessment process should therefore support prioritization, not merely generate an undifferentiated list of findings.
Enterprise governance must translate written AI policies into enforceable controls.
This includes defining which AI applications, models, MCP servers, Skills, and configurations are approved.
It also requires establishing restrictions on personal accounts, excessive permissions, and components that have not passed appropriate security review.
Backslash supports centrally managed policies, allowlisting, and controls designed to restrict unauthorized components and unsafe configurations.
A useful governance model should recognize that different engineering teams may have different operational requirements.
The objective is to preserve legitimate access while preventing uncontrolled extensions of agent capabilities.
For leadership, this provides a more scalable alternative to handling every AI adoption request as an isolated exception.
Risk assessment and configuration policies are necessary, but agent behavior must also be monitored during execution.
An agent may encounter malicious instructions or attempt an action that violates organizational policy after its initial configuration has been reviewed.
Backslash provides runtime monitoring and inline protection designed to identify and block risky behavior, including data exfiltration attempts, privilege escalation, prompt injection, and unauthorized actions.
This is an important distinction between simply knowing that a risk exists and being able to intervene when that risk materializes.
An effective security architecture should evaluate agent actions against their expected behavior and organizational policy.
This allows legitimate AI-assisted work to continue while introducing safeguards against actions that exceed approved boundaries.
Finally, organizations need evidence explaining what AI agents did and why.
Backslash provides activity tracing across prompts, processes, tool calls, and resulting actions.
These records can help security teams reconstruct incident sequences, investigate policy violations, and support compliance activities.
The value is not limited to post-incident analysis.
Traceability helps organizations evaluate whether their AI governance policies are operating as intended.
It can also identify recurring configuration problems or workflows requiring improved controls.
For senior management, this creates a foundation for reporting on AI security posture using observable activity rather than assumptions.
Backslash's October 2026 research offers practical evidence of the gap between AI adoption and AI security maturity.
Across assessed enterprise environments, employees used approximately 1.4 AI or coding agents per endpoint on average, excluding dynamically spawned subagents.
The research also identified personal AI account usage in every assessment where account usage was scanned and reported.
Unapproved or policy-violating models appeared in approximately two-thirds of environments where model usage was directly assessed.
Even a small deployment could contain meaningful exposure: an assessment involving six endpoints uncovered 31 policy violations.
These figures describe Backslash's assessed environments, not a statistically representative sample of every technology organization.
Nevertheless, they highlight an important management issue.
The number of approved applications is not a reliable measure of security maturity. The actual risk depends on how agents are configured, what resources they can access, and which controls operate during execution.
A CEO does not need to administer endpoint policies personally. However, executive leadership should ensure that AI adoption has clear ownership, measurable visibility, and enforceable security boundaries.
A practical review can begin with five questions:
If the organization cannot answer these questions with supporting evidence, it has an agentic endpoint governance gap.
The next step should be to establish an inventory, identify material risks, assign policy ownership, and implement appropriate monitoring and enforcement.
The business objective of securing AI agents is not to discourage developers from adopting more productive workflows.
It is to make those workflows sustainable.
An organization that understands its agentic fabric can distinguish approved activity from unacceptable risk, support legitimate engineering requirements, and respond when configurations or behavior change.
Backslash Security addresses this requirement through continuous discovery, risk assessment, centralized governance, runtime protection, and forensic tracing across developer and employee endpoints.
For technology leaders, the strategic principle is straightforward: AI innovation should scale alongside security visibility and control, not ahead of them.
Learn more about Backslash Agentic Endpoint Security and how enterprises can govern agentic AI across their development environments.
Enterprises should discover installed AI agents and associated components, assess their security posture, enforce centrally managed policies, protect against dangerous runtime actions, and maintain detailed activity records. The assessment must include MCP servers, Skills, hooks, plugins, models, configurations, and account identities because these components determine the agent's effective capabilities.
The risks identified in Backslash's research include unauthorized configurations, unapproved models, personal-account usage, excessive permissions, vulnerable or malicious agent components, credential exposure, prompt injection, and data exfiltration. Risk varies by workstation configuration and the resources accessible to the agent, even when the underlying tool is approved.
Traditional endpoint security may observe operating-system activity without understanding the AI-specific context that produced it. Agentic security adds visibility into instructions, models, MCP interactions, Skills, permissions, and tool calls. Backslash positions these capabilities as complementary to existing endpoint security rather than as a replacement.
Companies should maintain inventories, assess components before approval, identify excessive permissions and unsafe instructions, and apply centralized allowlisting or blocking policies. Continuous reassessment is also important because changing an MCP connection, Skill, or local configuration can change an agent's capabilities after the original application has been approved.
Executives can request evidence of inventory coverage, detected policy violations, remediation activity, enforcement coverage, and agent activity tracing. These measurements help establish whether the organization understands actual AI usage and can investigate or prevent risky behavior rather than relying exclusively on written policies.
No. The Backslash approach focuses on enabling approved AI use through visibility, governance, and protection. Security teams can evaluate the components and permissions used by agents, restrict activities that violate policy, and maintain oversight without imposing a blanket prohibition on legitimate AI-assisted development.

Backslash Security is the Agentic AI Endpoint Security platform. We enable enterprises to discover, govern, and protect the agentic AI fabric - every AI agent, MCP server, and Skill running on employee endpoints - securing agentic AI at enterprise scale and business velocity.



Privacy is important to us, so you have the option of disabling certain types of storage that may not be necessary for the basic functioning of the website. Blocking categories may impact your experience on the website. More information


